Cybersecurity
Cyber Insurance Requirements: What IT Controls Insurers Actually Want
Cyber insurance renewal forms commonly ask about MFA, backups and restore testing, endpoint protection, email security, security awareness training, and admin access. Here is what small businesses should know before applying or renewing.
Cyber insurance renewal forms commonly ask about multi-factor authentication (MFA) on email, remote access, and admin accounts; endpoint protection such as EDR; backups and restore testing; security awareness training; and who has admin access. Some also ask whether you have a written business continuity or recovery plan. The specifics vary by carrier, so read your own application before you answer anything.
If you can’t honestly answer yes to these controls, fix them before you apply. The answers are yours to sign.
What do cyber insurers require?
Applications are how an insurer measures risk, so the questions follow the weak spots attackers use again and again: no MFA, thin endpoint protection, backups nobody has tested, and no plan when an incident starts.
Here is what renewal forms commonly ask about:
Multi-factor authentication (MFA) on email accounts, remote access (VPN and RDP), and administrative or privileged accounts. MFA stops most automated password attacks. If your staff reaches email or company systems remotely without a second factor, expect that to be an early question on any application.
Endpoint protection, and often EDR (endpoint detection and response) by name. Signature-based antivirus misses attacks it has never seen. EDR watches behavior, which is why applications increasingly ask for it.
Backups and restore testing. The word “tested” matters. An untested backup is a backup-shaped assumption. Ransomware often goes after connected backups, so applications ask whether a copy is kept separate and whether you have actually restored from it. A restore test you ran once, three years ago, documented somewhere no one can find, doesn’t answer that.
Security awareness training for all staff. Phishing is still one of the most common ways attackers get in, which is why applications increasingly ask for recurring training, not a one-time video.
Admin access. Who has administrator rights, and whether that list is reviewed.
Some applications also ask whether you have a written business continuity or recovery plan and whether anyone has tested it. Whatever you call it, a written plan for incidents is worth having. It doesn’t have to be elaborate. It does have to exist, and people have to know where it is.
For a baseline on the security controls your business should have in place regardless of insurance, the cybersecurity guide for small business covers the fundamentals in practical terms.
Why do applications ask about MFA?
Because stolen credentials are one of the most common ways in. Microsoft’s own research found MFA cut the risk of account compromise by more than 99% (Microsoft Research). Applications tend to ask where MFA is on, not just whether you have it:
- Email accounts (Microsoft 365, Google Workspace)
- Remote access: VPN, RDP, any path into your network from outside
- Administrative and privileged accounts, the ones that reach your most sensitive systems and data
Some applications treat missing MFA on admin accounts as a deal-breaker. Ask your agent how your policy handles it.
The good news: MFA is one of the cheaper controls to put in place. Microsoft 365 and Google Workspace include basic MFA at no extra cost. The barrier is organizational, not financial. Getting staff to enroll and accept the extra step takes the work.
What controls do underwriters look at most closely?
Insurers price risk, and the application is how they measure it. These are the controls underwriters tend to look at most closely. How any of them affects your price is up to your carrier.
MFA beyond admin accounts. Many applications ask about MFA beyond admin accounts. Extending it to every account costs little and closes a common way in.
EDR versus basic antivirus. EDR watches behavior, not just known malware, which is why applications increasingly ask for it by name.
Backup isolation and verified restores. Applications often ask whether backups are isolated and whether you have tested a restore.
A written business continuity or recovery plan. Some applications ask whether you have a written plan and whether it has been tested.
The cost comparison for managed IT services is worth reading if you are trying to understand what professional IT support costs.
What happens if an answer is wrong?
If the answers on an application turn out to be wrong, an insurer may have grounds to deny a claim or cancel the policy. Your agent or an attorney can tell you how that works for your policy.
Applications ask specific questions about specific controls. “Do you have MFA on all remote access?” is a yes or no question, and the signature on it is yours. We do not fill in, review, or submit your form.
How do you prepare for a cyber insurance application or renewal?
Preparing comes down to five steps: pull the application early, check your controls honestly, close the gaps, keep records, and get an outside look before the renewal conversation starts. Hampton Roads businesses that treat the application as a security roadmap, not a last-minute form, give themselves time to fix what they find.
Step 1: Pull the application before you need it. Most small businesses see their cyber insurance application for the first time when it arrives for renewal. By then there is often no time to put missing controls in place. Ask your agent for it early. Some carriers post theirs publicly.
Step 2: Check your current controls honestly. Not where you think you are. Where you actually are. Do all staff have MFA enrolled on their email accounts? All of them, including the part-time bookkeeper and the owner? Is remote access behind a VPN with MFA? When did you last restore from backup to see that it works?
Step 3: Close the gaps before you apply. MFA, endpoint protection, tested backups, and patching discipline are worth having because they reduce your actual risk, not because a form asks. Questions about coverage go to your insurance agent.
Step 4: Keep records. Applications ask not just whether you have controls but how they are managed. A written patching policy, training completion records, backup restore logs, and a plan for incidents are evidence that your security program is real and not just a verbal claim.
Step 5: Get an outside look before your renewal conversation. A technical review can show gaps while there is still time to fix them.
Helix Stax works with Hampton Roads small businesses on the cybersecurity compliance controls that cyber insurance applications ask about: MFA deployment, endpoint protection, backup verification, and records of which controls are running. If you are not sure where your gaps are, start with the free Helix Score for a three-minute orientation. When you want a full picture, book a free IT assessment.
We are not an insurance agency or broker. We do not fill in, review, or submit insurance applications. The answers and the signature are yours.
Read the application before you buy or renew, and answer only what is true today. Questions about coverage go to your insurance agent.
Why Helix Stax
Putting security controls in place and keeping records of them are the same work when done right, which is why we do not treat cyber insurance readiness as a separate project. Helix Stax is a full-stack IT consulting firm in Hampton Roads covering MFA rollout, endpoint protection, backup verification, patching, and the records that show which controls are running, alongside the vCIO strategy that keeps those controls current between renewals. One team owns the whole picture instead of handing you off between a security vendor and a compliance consultant.
Renewal season is a reasonable time to get a second set of eyes on your controls.
Read more
Cybersecurity
The Cyber Insurance Questionnaire, Question by Question
A plain-English walk through the cyber insurance questionnaire: what each question asks, what to have on hand, and who signs. For firms of 10 to 50 users.
Cybersecurity
Do I Still Need IT Support If I Use AI Tools?
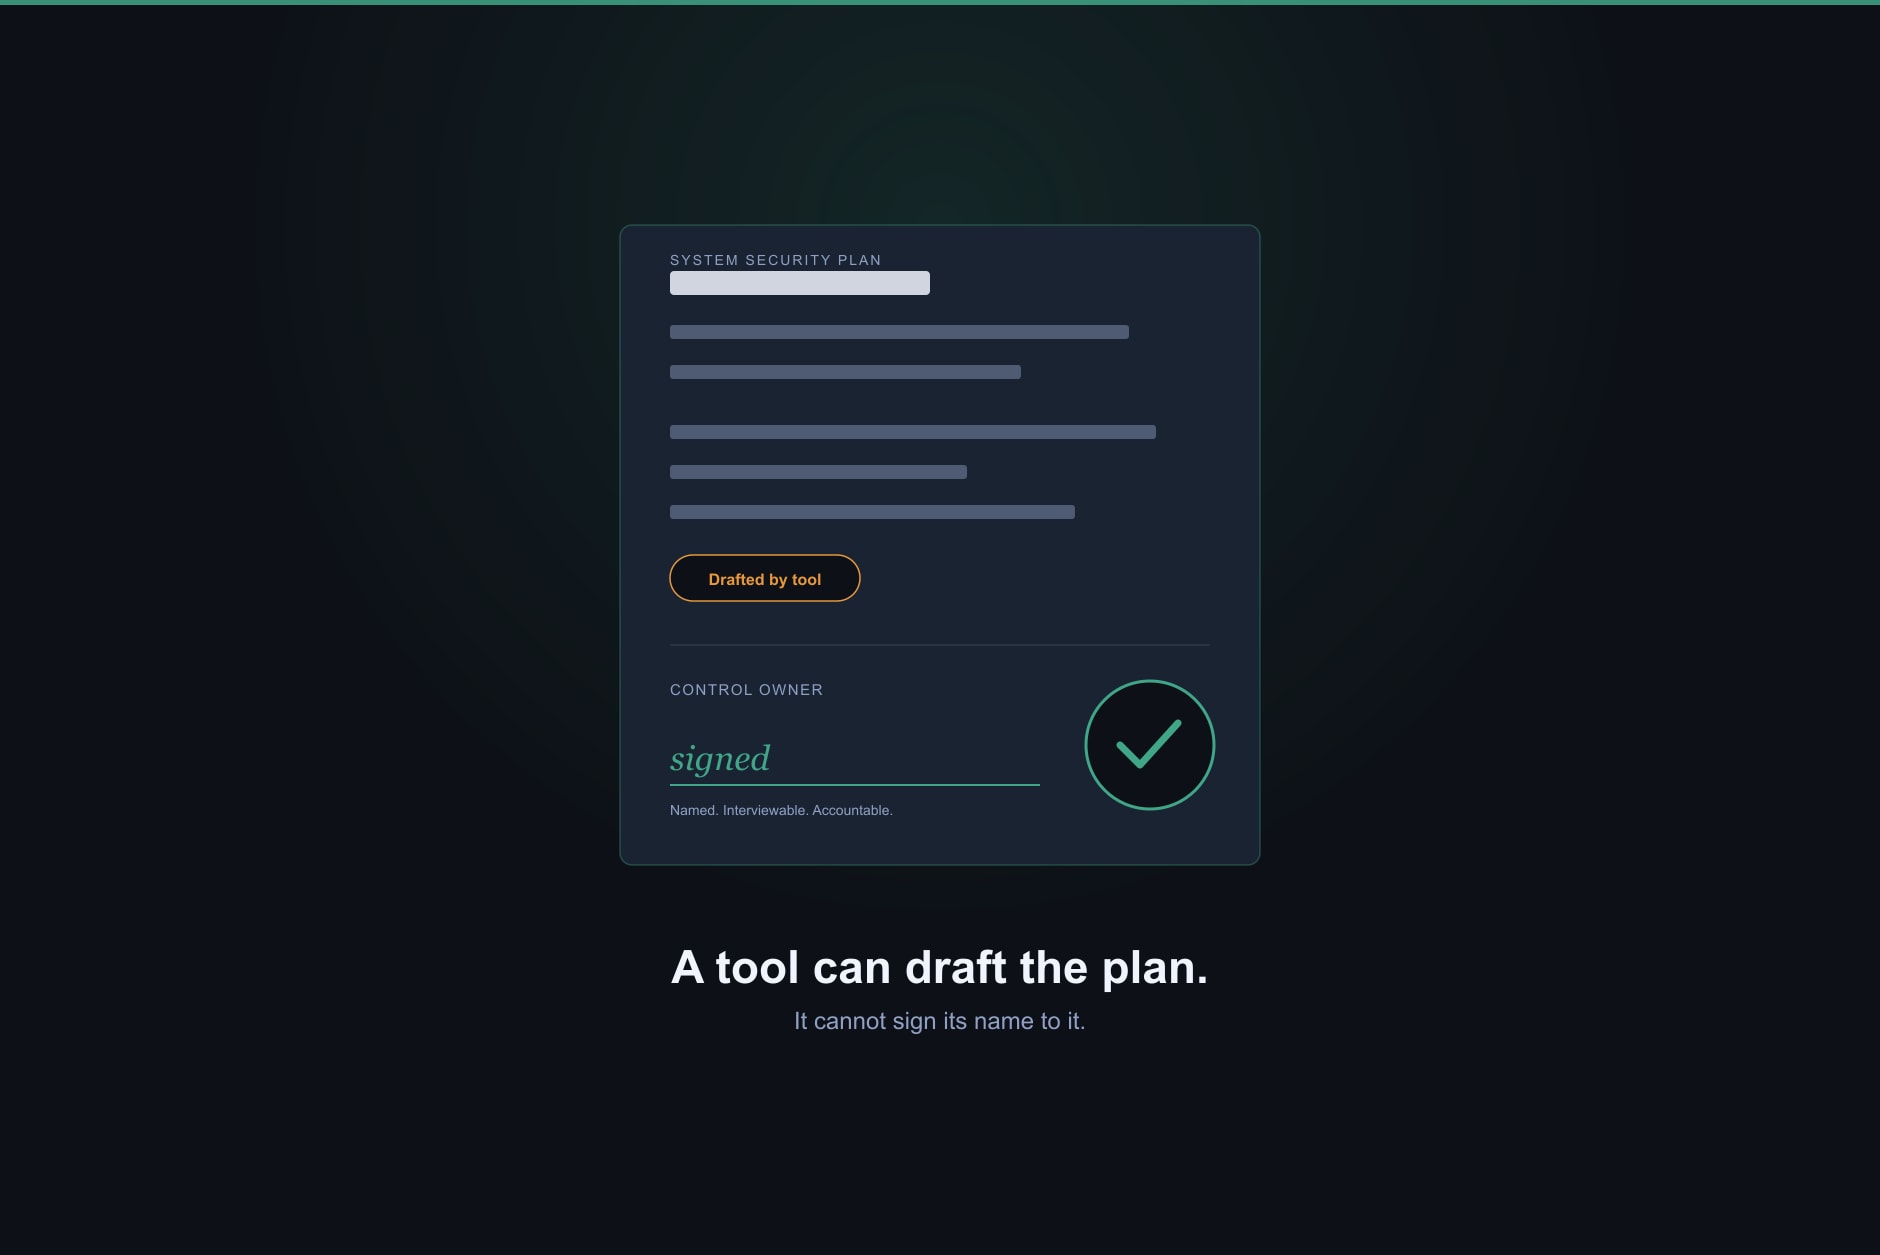
Yes. AI tools can flag issues and draft documentation, but a CMMC or NIST 800-171 auditor needs a named human control owner, not a chatbot. Here's what AI can and can't replace.
Cybersecurity
Network Security Assessment Checklist: What to Inspect and Which Tools Actually Help
A network security assessment checklist covering perimeter, segmentation, wireless, identity, endpoints, logging, and patching, plus what the assessment tooling landscape looks like and how to read your results.
Frequently asked questions about Helix Stax managed IT services
Renewal forms commonly ask about MFA on email, remote access, and admin accounts; backups and restore testing; endpoint protection; email security; security awareness training; and admin access. Some forms ask whether you have a written business continuity or recovery plan. Questions vary by carrier, so read the application early. Your carrier and agent decide what your answers mean for your policy.
A readiness checklist lists the controls an application is likely to ask about: MFA enabled, endpoint protection deployed, backups tested, admin accounts limited, staff trained, and records kept. Use it before you apply so each answer matches what is actually running. We do not fill in, review, or submit your form.
That is a question for your insurance agent. Our job is the security side: knowing which controls are actually in place before you answer an application.
Cost depends on factors such as revenue, industry, claim history, the data you hold, the limit, and the deductible. Only a carrier or agent can quote it. We can't, and we don't predict how any control changes a price.
Exclusions vary by policy, and only your agent or carrier can tell you what yours covers.
Yes. Applications we have seen ask about MFA on email, remote access, and admin accounts. How MFA affects your price or eligibility is up to your carrier. For MFA basics, see our small business cybersecurity checklist.
Renewal forms commonly ask about MFA, backups and restore testing, endpoint protection, email security, security awareness training, and admin access. Some ask whether you have a written business continuity or recovery plan. Your carrier and agent decide what those answers mean for your policy.
If the answers on an application turn out to be wrong, an insurer may have grounds to deny a claim or cancel the policy. Your agent or an attorney can tell you how that works for your policy.
Ask for the application early, then compare each question to what is actually running. Check MFA, endpoint protection, backup restore testing, patching, and admin accounts. Fix gaps before you sign when you can, and keep screenshots, reports, and training records. The answers and the signature are yours. We do not fill in, review, or submit your form.
There is no single standard. Each application sets its own questions. Renewal forms commonly ask about MFA, backups, restore testing, endpoint protection, email security, security awareness training, and admin access. Your carrier and agent decide what your answers mean for your policy.